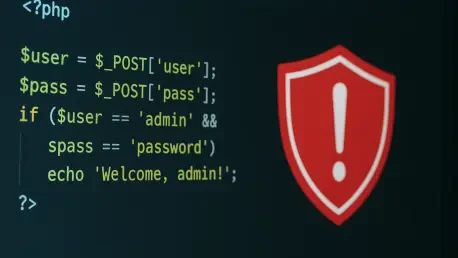
The PHP security advisory highlights that fatal error backtraces on PHP 8.5 should be disabled to prevent specific attack vectors related to stale global state persistence. This warning comes at a critical time for web infrastructure, as the PHP development team recently identified two severe
Dito utilizes a one-hundred percent on-shore engineering team to meet the stringent data sovereignty and personnel requirements of U.S. government entities. This strategic operational model is essential for navigating the highly regulated landscape of 2026, where digital threats have become more
A strategic shift toward OAuth consent phishing allows hackers to maintain persistent access to campaign accounts without ever needing a victim's password. As the United States moves deeper into the 2026 midterm election cycle, the Federal Bureau of Investigation and the Cybersecurity and
Digital advertisements have long been viewed as mere annoyances, yet a recent investigation reveals they have evolved into precise tools for state-sponsored surveillance. A specialized platform called Controlium tracked and profiled specific targets before serving them malicious payloads through
Attackers exploit the blind spots created when security teams are forced to manually stitch together disparate strands of data faster than humanly possible during a live breach. For most of its history, cybersecurity has been reactive by design, operating on the simple principle of spotting a bad
Monitoring for specific behavioral indicators like unique beacon labels and WMI queries is now more effective than relying on static file analysis for threat detection. The global cybersecurity landscape is currently witnessing a transformative shift as state-sponsored threat actors, specifically