Security breaches occur when an AI model is induced to treat malicious instructions extracted from a code sandbox as its own internal reasoning, thereby circumventing restricted system instructions. In the current landscape of 2026, these sophisticated cryptographic injections have fundamentally
The era of simple, flood-oriented botnets has largely transitioned into a more calculated landscape where persistence and operational depth define success for threat actors targeting the internet of things. The use of port 443 for command-and-control communications enables Evooo1Bot to blend its
A sophisticated supply chain attack recently demonstrated that poisoned containers could weaponize the very tools meant to ensure software security and quality. This alarming campaign, uncovered by threat intelligence specialists, targeted LiteLLM and the widely used vulnerability scanner Trivy to
The development of specialized proof-of-concept tools has automated the extraction of BTR.sys from Defender updates and the subsequent creation of encrypted configuration blobs for unauthorized file removal. This discovery highlights a profound shift in how threat actors view the inherent trust
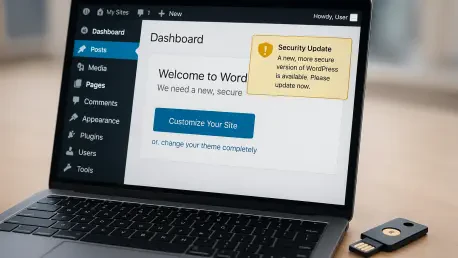
Under the Australian Notifiable Data Breaches scheme, a compromise involving hijacked administrative two-factor credentials triggers mandatory reporting obligations that small businesses often overlook until a breach occurs. This reality underscores the gravity of the recently identified
Defensive architectures in 2026 have shifted toward a state of perpetual vigilance, where autonomous platforms verify exploitability and initiate remediation workflows in real-time. The old model of periodic vulnerability scanning has been relegated to the archives of tech history, replaced by