The traditional paradigm of cyber exploitation has undergone a radical transformation as malicious actors now deploy sophisticated artificial intelligence to automate the labor-intensive process of victim valuation and digital asset analysis. Security researchers recently identified a potent new
The sophisticated nature of modern cyberattacks often targets the very mechanisms designed to protect corporate networks, as seen in the recent discovery of a critical security flaw within SonicWall perimeter devices. This vulnerability, tracked as CVE-2026-19868, represents a significant threat to
ARTEX relies heavily on ScopeSentry integration to feed target data like domains and open ports into its automated vulnerability scanning modules. This sophisticated ecosystem, which emerged in mid-2026, functions as an integrated penetration-testing platform designed to minimize the manual effort
A robust security architecture must validate that the relying party ID matches the application's domain to prevent origin mismatches during the sensitive WebAuthn registration phase. This requirement is not merely a suggestion but a fundamental pillar of the FIDO2 standard, ensuring that
Security flaws like CVE-2024-50629 and CVE-2024-10445 represent significant risks for organizations that have failed to move to the latest DSM security patches. These vulnerabilities allow attackers to bypass traditional defenses and gain unauthorized access to data stored on network-attached
The shift toward consumption-based pricing models by frontier AI providers has fundamentally changed how enterprises manage their cybersecurity posture. As the initial excitement of 2026 settles into a more disciplined operational phase, many organizations are re-evaluating the "tokenmaxxing"
The discovery of stolen VPN profiles and password lists within compromised tenants highlights the severe risks associated with neglected service-principal permissions. When a major cybersecurity campaign surfaced in late 2026, it revealed a sophisticated operation targeting over 27 organizations
Google has severed all professional ties with Videostrong Technology after discovering the firm intentionally built backdoors into over a million Android-based streaming devices. This unprecedented breach of trust highlights a sophisticated supply-chain compromise that transformed mundane consumer
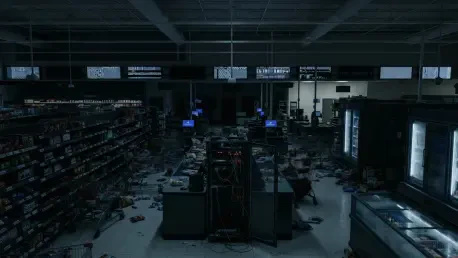
The intentional thermal spiking of supermarket freezers demonstrates how digital breaches now result in immediate, tangible, and costly physical consequences. For years, the retail sector focused primarily on protecting credit card data, but a wave of incidents across Europe has proven that the
The malware achieves persistence by hiding legitimate Windows Media Player components in the ProgramData folder and configuring them to load secondary malicious libraries. This sophisticated method of staying hidden is just one component of a broader campaign that exploits the current global
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61 62 63 64 65 66 67 68 69 70 71 72 73 74 75 76 77 78 79 80 81 82 83 84 85 86 87 88 89 90 91 92 93 94 95 96 97 98


