The United States has already restricted the import of certain foreign network routers, signaling a shift toward mandatory compliance that South Korean regulators have yet to match. This discrepancy highlights a growing gap between the rapid adoption of smart home technology and the legal
Organizations must pivot toward a prevention-based approach to counter the velocity and scale of modern, AI-driven automated cyber threats. The digital landscape has fundamentally shifted as malicious actors leverage generative models and automated scanning to identify and exploit vulnerabilities
Systemic cybersecurity failures have been linked to worsened survival rates for cardiac arrests due to delayed emergency responses and diagnostic bottlenecks in compromised hospitals. The rapid digitalization of healthcare has revolutionized the surgical landscape, moving the field away from
Attackers successfully exploited the psychological pressure of a twenty-four-hour deletion deadline to compel users to interact with malicious links hidden in fake service alerts. This specific campaign highlights a growing trend in the cyber threat landscape where actors no longer wait for a
The ubiquity of Quick Response codes across modern urban landscapes has transformed the average smartphone into a high-stakes target for sophisticated cybercriminals in 2026. From digital restaurant menus to contactless payment portals at public transit hubs, these matrix barcodes provide a
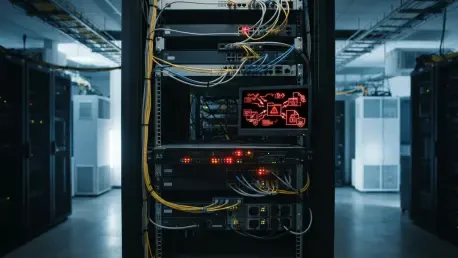
A critical insecure deserialization bug identified as CVE-2026-20131 allows remote attackers to execute arbitrary Java code with root privileges on the Cisco Secure Firewall Management Center interface. This vulnerability represents a fundamental breakdown in how the management console processes
While custodial mobile apps remained largely unaffected, the recent string of exploits highlights the technical burdens placed on those who choose to run their own sovereign infrastructure. For many enthusiasts, the appeal of Bitcoin has always been the ability to act as one's own bank, but recent
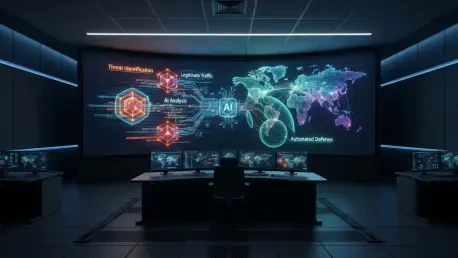
The shift toward AI-driven orchestration serves as a vital tool for reducing analyst burnout by automating the triage of thousands of standard security alerts. This directive, established under Binding Operational Directive 26-04, forces a fundamental rethinking of how the United States federal
Modern software development relies on an intricate web of automated trust that, while efficient, has recently become the primary target for one of the most widespread credential-harvesting operations seen this year. The digital supply chain is currently facing a silent siege that exploits the very
The requirement for IT administrators to immediately inventory and replace certificates issued by affected G2C authorities highlights the real-world impact of CA mismanagement. When a foundational entity responsible for verifying the identity of websites and encrypting internet traffic suffers a
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61 62 63 64 65 66 67 68 69 70 71 72 73 74 75 76 77 78 79 80 81 82 83 84 85 86 87 88 89 90 91 92 93 94 95 96 97 98 99 100 101 102 103


