The pursuit of digital sovereignty through local artificial intelligence has inadvertently created a sprawling playground for sophisticated cyberattacks, exposing the very secrets that users intended to protect from the public cloud. As organizations shift toward local large language model (LLM)
The quiet efficiency with which a single malformed network packet can dismantle the perimeter of a global enterprise has never been more apparent than with the discovery of CVE-2026-0300. This guide serves to illuminate the dangers posed by this critical vulnerability while providing a roadmap for
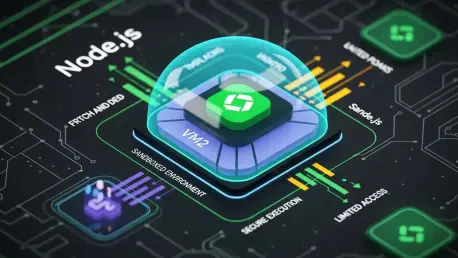
The delicate balance between allowing users to execute custom scripts and maintaining the impenetrable integrity of a host server has never felt more precarious than it does in today’s interconnected cloud environment. Within the Node.js ecosystem, the vm2 library was once heralded as the
The modern threat landscape has undergone a fundamental transformation, shifting away from the era of simple, transactional data breaches toward a model of long-term persistent occupation. Recent analysis reveals that sophisticated adversaries are no longer satisfied with quick smash-and-grab
A simple four-byte overwrite in the kernel memory management of a Linux system can strip away the security boundaries of an enterprise server in seconds, turning a standard user into a system administrator. This critical logic flaw, tracked as CVE-2026-31431 and nicknamed Copy Fail, represents a
When a single vulnerability can jeopardize tens of millions of websites overnight, the foundational security of the internet is no longer a theoretical concern—it is a critical emergency. With the Cybersecurity and Infrastructure Security Agency (CISA) sounding alarms over near-perfect severity