A robust security architecture must validate that the relying party ID matches the application's domain to prevent origin mismatches during the sensitive WebAuthn registration phase. This requirement is not merely a suggestion but a fundamental pillar of the FIDO2 standard, ensuring that
Recent benchmarks from the Agent Security League reveal that over eighty percent of functionally correct solutions produced by AI coding agents still contain hidden security vulnerabilities. This startling reality has fundamentally altered the software development landscape as organizations
The Cloud Next-Generation Firewall has been upgraded with an advanced malware sandbox powered by WildFire technology to counter threats moving at machine-assisted speeds. This evolution is central to the Fairwind Program, an initiative that integrates autonomous agents to hunt threats and remediate
A simple incoming voice call on a smartphone, an action performed millions of times a day, recently transformed into a silent gateway for unauthorized remote access. Security researchers at the startup NebuSec identified a critical vulnerability within Telegram for Android that allows malicious
Employees driven by a productivity-first mindset frequently bypass official procurement processes to integrate cutting-edge tools that lack organizational visibility and security oversight. This phenomenon, which has accelerated significantly since the beginning of 2026, stems from a desire to
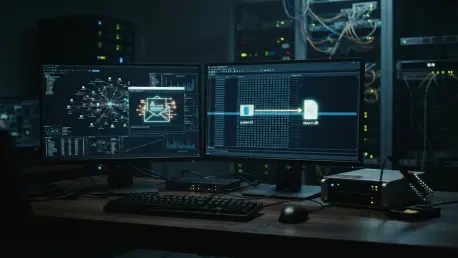
The malware achieves persistence by hiding legitimate Windows Media Player components in the ProgramData folder and configuring them to load secondary malicious libraries. This sophisticated method of staying hidden is just one component of a broader campaign that exploits the current global
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61