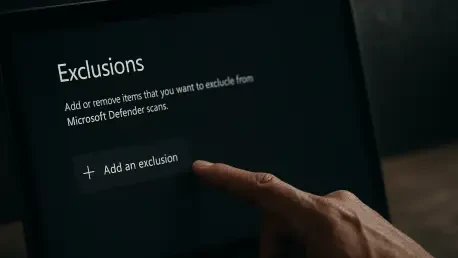
The strategic ROI for a threat actor increases significantly when they can download and unpack ransomware within a zone explicitly ignored by Microsoft Defender. This method of bypassing security protocols represents a sophisticated shift in cyber-adversary tactics, where the tools designed for protection are surreptitiously turned against the host system. By securing elevated privileges, attackers can manipulate Microsoft Defender Antivirus (MDAV) exclusion lists to carve out safe zones for their malicious payloads, ensuring that high-risk activities remain invisible to the primary defense engine. Central to this strategy is the exploitation of the HideExclusionsFromLocalAdmins registry setting, a configuration that masks unauthorized changes from the very personnel responsible for maintaining system integrity. This technique effectively blinds security teams, allowing malicious software to persist while the antivirus reports a clean bill of health. In an environment where automated alerts are the first line of defense, this subtle subversion creates a dangerous gap that traditional monitoring often fails to bridge during initial phases.
The Strategic Subversion of Administrative Features
Weaponizing Trust: The Mechanics of Strategic Exclusions
Microsoft Defender exclusions exist to optimize performance by instructing the scan engine to ignore specific files or folders that are known to be safe but resource-intensive. These often include database files, high-traffic application directories, or specialized developer tools that might otherwise trigger false positives or performance bottlenecks. However, when an adversary gains administrative control, this feature is repurposed into a powerful evasion tool. By defining a directory as excluded, the attacker creates a sanctuary where malware can reside without the risk of real-time detection. This subversion of trust is particularly effective because the security software remains active and operational across the rest of the system, providing a false sense of security while a critical blind spot is actively exploited. This strategic weaponization allows sophisticated actors to bypass the standard heuristics and signature-based detection mechanisms that would normally intercept unauthorized code execution.
Attackers often prioritize path and extension exclusions because they provide the highest tactical return on investment for long-term persistence. For instance, excluding a broad path like the entire system drive or a common temporary directory enables the execution of various malicious scripts and binaries without triggering any automated response from the defensive stack. These safe zones allow for the deployment of info-stealers, ransomware, or lateral movement tools that would otherwise be flagged immediately. Furthermore, extension-based exclusions, such as those targeting .vbs or .ps1 files, allow attackers to run scripts that are essentially invisible to the antivirus engine’s scanning logic. By carefully selecting these parameters, threat actors ensure their activities blend into the expected noise of a busy system, making it nearly impossible for standard monitoring solutions to identify the presence of malicious intent. This calculated approach minimizes the footprint of the attack while maximizing the duration of the unauthorized access within the target network.
Tactical Execution: Entry Points and Real-World Precedents
The injection of unauthorized exclusions is achieved through multiple administrative interfaces, including Intune, Group Policy Objects (GPOs), and Windows Management Instrumentation (WMI). This variety of entry points complicates the defensive posture, as security teams must monitor a wide array of potential modification vectors to catch tampering. Attackers often leverage built-in Windows tools to implement these changes, making the activity appear like legitimate administrative maintenance. For example, a PowerShell command executed with elevated rights can silently add a path to the exclusion list in seconds, while a GPO modification can push these changes across an entire domain. Because these tools are integral to modern system management, distinguishing between a valid administrative update and a malicious configuration change requires deep contextual analysis and robust logging. The ability to use existing management frameworks to impair security products is a hallmark of current Living off the Land strategies that dominate the modern threat landscape.
Real-world campaigns have frequently demonstrated the efficacy of this approach in high-stakes environments. The GootKit malware family, for instance, has been observed utilizing WMI to inject Defender path exclusions, effectively carving out a hidden niche for its secondary payloads. Similarly, the WhisperGate malware, known for its destructive capabilities, utilized PowerShell to exclude entire drives from scanning during its initial execution phase. These actions align with the MITRE ATT&CK framework for impairing defenses, as they allow the malware to operate without disabling the antivirus service entirely. Disabling the service is often a noisy event that triggers immediate alerts in a Security Operations Center, whereas a hidden exclusion allows the software to continue reporting a healthy status. This preference for stealth over total destruction highlights the evolution of adversary tradecraft, where maintaining a low profile is prioritized to ensure that the primary objectives of the intrusion are met before detection occurs.
Mechanisms of Evasion and Concealment
Registry Manipulation: Creating Administrative Blindness
A critical component of this evasion strategy involves the manipulation of the HideExclusionsFromLocalAdmins registry key, located within the Microsoft Windows Defender policy settings. When this specific value is enabled, any exclusions added to the system remain active but are suppressed from the standard user interfaces. This means that a local administrator checking the Windows Security GUI or using common PowerShell commands like Get-MpPreference will see an empty or seemingly clean exclusion list. This creates a state of profound administrative blindness, where the personnel responsible for endpoint security are misled into believing the environment is properly hardened. The configuration changes are effectively hidden in plain sight, as they continue to protect malicious files from scanning while remaining invisible to the very tools used for auditing. This level of deception is particularly dangerous because it bypasses the manual verification steps that many security teams rely on during incident response or routine maintenance checks.
Beyond blinding human administrators, this registry manipulation can also impair the effectiveness of automated security tools and third-party monitoring agents. Many security solutions rely on standard system queries to verify the configuration of the native antivirus; if these queries are suppressed or return incomplete data due to the concealment policy, the entire security stack may be compromised. This creates a scenario where a system reports a Healthy status on central management dashboards while a massive security hole is being exploited. Even SYSTEM-level queries, which are typically granted the highest level of access, can be hampered by these policy settings if they are not specifically designed to look for these hidden keys. The result is a false positive for system health that can persist for weeks or months, giving attackers ample time to move laterally, exfiltrate sensitive data, or prepare for a final destructive phase. This concealment technique represents a significant hurdle for organizations that rely solely on automated health reports.
The Shift Toward Partial Impairment: Adversary Behavior in 2026
There is a clear and growing trend among threat actors in 2026 to move away from aggressive all-or-nothing methods, such as completely disabling security services, in favor of partial impairment strategies. By keeping the security product running while selectively disabling its most critical functions, attackers can significantly extend their dwell time within a network. This shift reflects a deeper understanding of modern detection capabilities, where a stopped service is a high-priority alert that demands immediate investigation. In contrast, a lobotomized antivirus that appears active but ignores the attacker’s specific folders is much harder to detect through traditional means. This move toward subtle impairment is part of a broader transition toward Living off the Land techniques, where the administrative tools provided by the operating system are turned into liabilities. This approach forces security teams to evolve their monitoring strategies, moving past simple service checks to more granular verification of internal security configurations and policy integrity.
The integration of these evasion techniques into the standard toolkit of modern adversaries demonstrates a shift toward more resilient and stealthy operations. In the current landscape of 2026, the success of a cyberattack often hinges on the ability to remain undetected for as long as possible, and partial impairment provides the perfect mechanism for this. By subverting the native administrative features of the Windows operating system, attackers can maintain a persistent presence that is resistant to common remediation efforts. This evolution in tradecraft underscores the necessity for defenders to adopt a more skeptical view of their security dashboards. Relying on a green Healthy icon is no longer sufficient when the underlying configuration can be manipulated to create invisible gaps in protection. As these techniques become more common, the focus must shift toward verifying the actual state of the system through independent telemetry and deep-level auditing that can bypass the deceptive policies implemented by sophisticated threat actors.
Strengthening Defenses Against Stealthy Manipulation
Registry-Level Telemetry: The Essential Protective Layer
To effectively counter these stealthy tactics, organizations must prioritize registry-level telemetry as a core component of their monitoring strategy. Since every configuration change, whether initiated via GPO, WMI, or PowerShell, is ultimately recorded in the Windows Registry, monitoring specific keys is the most reliable way to maintain a complete view of system health. Security teams should implement real-time alerts for any modifications to the Microsoft Windows Defender exclusion keys or the concealment policy settings. This level of visibility ensures that even if an exclusion is hidden from the standard GUI, it will still be flagged by the monitoring agent during the registry write event. By focusing on the underlying data structures rather than the high-level management interfaces, defenders can maintain an accurate picture of the endpoint’s defensive state. This approach bridges the visibility gap created by concealment policies and provides the raw data necessary to identify unauthorized changes before they can be exploited.
In addition to technical monitoring, maintaining the principle of least privilege is a vital defense against the implementation of these evasion techniques. Because an attacker must possess administrative or SYSTEM privileges to modify Defender exclusions or toggle concealment settings, limiting the number of users with these rights significantly reduces the attack surface. Organizations should conduct regular audits of privileged accounts and move toward a model of just-in-time administration where elevated rights are granted only for specific tasks and for a limited duration. By preventing an initial foothold from escalating into full administrative control, the risk of defensive impairment is drastically lowered. This focus on identity and access management complements technical monitoring by addressing the root cause of the vulnerability. When administrative access is tightly controlled, the ability of an adversary to manipulate the security configuration of an endpoint is severely restricted, thereby forcing them to use noisier and more easily detectable methods.
Establishing Baselines: Strategic Auditing and Policy Validation
Establishing a rigorous security baseline for approved exclusions is a fundamental step in detecting unauthorized modifications. Any deviation from this baseline, particularly the addition of broad paths, wildcard characters, or exclusions targeting user-writable folders, should be treated as a high-fidelity indicator of a potential compromise. Security teams must ensure that they have a clear inventory of all legitimate exclusions required for business operations and use this as a reference point during routine audits. Furthermore, the practice of merging local exclusions with centrally deployed corporate policies should be carefully reviewed. If local administrators are allowed to add their own exclusions, an attacker who gains local rights can blend their malicious entries with legitimate ones, making detection far more difficult. Disabling local policy merging ensures that the security configuration remains consistent across the environment and is only controlled by authorized central management tools, thereby eliminating a common vector for impairment.
The investigation into hidden Microsoft Defender exclusions revealed that the operational status of an antivirus product was not a definitive metric for security. It was determined that a system could report a healthy state while simultaneously being configured to ignore the very directories where active breaches were unfolding. To address these findings, administrators implemented proactive registry monitoring and established strict baselines for all defensive configurations. They recognized that the integration of concealment policies represented a significant evolution in adversary tradecraft, necessitating a move toward deep-level system auditing. By prioritizing the principle of least privilege and validating policy integrity through independent telemetry, security teams successfully reduced the impact of partial impairment strategies. Ultimately, the transition to a more skeptical and data-driven approach to endpoint health ensured that hidden vulnerabilities were identified and remediated. These actions provided a more resilient defense against the sophisticated evasion techniques encountered in the current threat landscape.