Assessing the State of Software Supply Chain Security and CI/CD Vulnerabilities
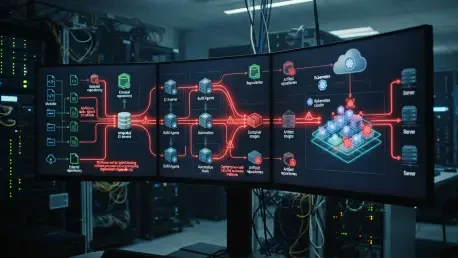
Modern security teams often focus on protecting the castle walls while neglecting the automated couriers that carry the keys to the kingdom through the front gate via continuous integration pipelines. As the shift toward rapid deployment accelerates, GitHub Actions has transformed from a mere convenience into the central nervous system of contemporary DevOps environments. This reliance creates a paradox where the very tools meant to increase efficiency also introduce profound risks. Automated workflows require extensive permissions to interact with cloud providers, making them a high-value target for anyone looking to bypass traditional perimeter defenses.
The persistent issue of secrets sprawl remains a primary catalyst for sophisticated attacks against private repositories. Developers frequently embed sensitive credentials, including API keys and database passwords, into their code or repository settings under the mistaken assumption that privacy equals security. Threat actors recognize that a single private repository often contains enough identity metadata to compromise an entire corporate infrastructure. This realization has shifted the offensive focus from traditional infrastructure exploitation toward the identity and access management layer of the development pipeline.
Recent observations of the Gheist campaign highlight the massive scale of these risks, specifically concerning the exploitation of Personal Access Tokens. By leveraging these stolen tokens, attackers have successfully breached over 850 accounts, affecting everything from personal side projects to high-stakes enterprise environments. The impact of such a campaign is not merely theoretical; it represents a systematic harvesting of sensitive data that undermines the foundational trust required for collaborative software development.
Evolution of Stealthy Data Exfiltration Trends in DevSecOps
Emerging Techniques in Workflow Manipulation and Log-Based Exfiltration
There is a visible transition occurring as attackers move away from deploying traditional malware toward living-off-the-cloud techniques. Within the GitHub ecosystem, this involves using native platform features to perform malicious actions, which often blends in with legitimate developer activity. By creating temporary branches and workflows, adversaries can execute code that appears standard to automated monitoring systems while secretly exfiltrating credentials through the very logs meant for debugging.
A particularly clever evolution involves the use of encoding methods like Base32 to circumvent built-in security features. GitHub naturally attempts to mask secrets in its Actions logs, but this protection relies on pattern matching the original secret value. When an attacker encodes a secret into a different format before printing it, the automated filters fail to recognize the sensitive data, allowing it to be recorded in plain sight. This method ensures that the stolen information is readily available for download through the GitHub API without alerting standard security triggers.
Furthermore, the adoption of branch-and-delete tactics has significantly complicated the task of forensic investigators. By creating a unique branch, running a malicious workflow, and then immediately deleting both the branch and the execution logs, attackers minimize their footprint in the audit trail. This rapid cleanup leaves security teams with a very narrow window to detect the breach, as the primary evidence of the intrusion disappears within seconds of the exfiltration being completed.
Market Projections for Security Tooling and Automated Guardrails
The rise in credential theft is driving a rapid expansion of the Secret Scanning and Posture Management market as organizations seek better visibility. From 2026 to 2028, investment in these specialized tools is expected to grow as businesses realize that static analysis alone cannot prevent token-based breaches. Modern solutions are increasingly focusing on the lifecycle of a secret, moving beyond simple detection toward active remediation and the enforcement of strict behavioral policies across the entire CI/CD environment.
There is also a strong push toward the adoption of OpenID Connect to replace long-lived secrets in automated workflows. By utilizing short-lived, identity-based tokens for cloud authentication, companies can significantly reduce the window of opportunity for an attacker who manages to compromise a repository. This shift represents a fundamental change in how access is managed, moving from a model of permanent trust to one of ephemeral, just-in-time authorization.
Current data suggests that while public repositories have received significant attention regarding security safeguards, private ecosystems remain disproportionately vulnerable. The frequency of token-based breaches in private environments often exceeds that of public ones because internal developers are less likely to follow rigorous security protocols. As more organizations move their critical workloads to the cloud, the disparity between these two environments will necessitate a more unified approach to secrets management.
Technical Obstacles and Defense Gaps in Private Repository Environments
Many enterprise environments currently struggle with a phenomenon known as approval fatigue, which severely limits the effectiveness of manual security reviews. When developers are constantly bombarded with requests to approve workflow runs, they often begin to treat these checks as a formality rather than a critical defensive measure. This human element creates a gap that attackers can exploit by inserting malicious code into seemingly routine updates, knowing that the likelihood of a detailed manual audit is low.
Private repositories often lack the rigorous workflow suppression policies that have become standard for public projects on GitHub. This discrepancy exists because organizations often prioritize developer velocity over strict security controls within their internal networks. Consequently, an attacker who gains access to a private token can often push new branches and trigger workflows without the same level of scrutiny that would be applied to a public contribution.
Overcoming the invisibility of internal branch creation requires a more proactive approach to monitoring audit logs and cloud role assumptions. Because the Gheist campaign operates with such speed, traditional reactive security measures are often insufficient. Organizations must implement automated triggers that alert security teams to any unusual branch patterns or rapid log deletions, especially when those actions are performed by automated user agents that do not match known developer profiles.
The risk extends even further when considering the use of self-hosted runners and their potential for lateral movement into cloud metadata services. If a malicious workflow runs on a self-hosted machine, it can search for local credentials or attempt to assume high-privilege roles associated with the underlying host. This creates a bridge between the software repository and the broader production environment, allowing an attacker to pivot from a simple code commit to a full-scale infrastructure compromise.
The Regulatory Landscape and Compliance Standards for Credential Management
Regulatory bodies like the SEC have increasingly tightened requirements for reporting secrets exposure and supply chain compromises. Organizations are now under significant pressure to provide transparent disclosures when their development pipelines are breached, particularly if the incident involves the potential theft of customer data or intellectual property. This regulatory climate is forcing a shift in how companies handle credential management, turning it from a purely technical concern into a core component of corporate governance.
Adhering to the Principle of Least Privilege has become both a security benchmark and a regulatory mandate for automation accounts. Compliance frameworks now require that every token and service account used in a CI/CD pipeline possesses only the minimum permissions necessary for its specific task. This limits the lateral movement an attacker can achieve after a successful initial compromise, effectively compartmentalizing different stages of the software development lifecycle.
Industry standards such as SOC2 and ISO 27001 are also evolving to mandate stricter audit log retention and token rotation policies. These certifications increasingly look for evidence that an organization is not only detecting breaches but also maintaining the historical data necessary to conduct a thorough impact analysis. As these standards mature, they are pushing the entire industry toward the deprecation of classic Personal Access Tokens in favor of more secure, fine-grained access methods.
Future Directions in Pipeline Integrity and Threat Detection
The integration of AI-driven anomaly detection is poised to become a standard defense against suspicious user agents and automated harvesting tools. By analyzing the behavior of API requests and identifying patterns that deviate from normal human activity, these systems can flag potential threats in real-time. This capability is essential for identifying campaigns like Gheist, which rely on the speed and scale of automation to overwhelm traditional security defenses.
We are moving toward episodic CI/CD environments where runners are entirely ephemeral and access is strictly short-lived. In this model, the infrastructure used to build and deploy code exists only for the duration of a single job, leaving no persistent environment for an attacker to exploit. This architectural shift significantly raises the bar for adversaries, as they must execute their entire attack within the lifespan of a single, highly monitored process.
Potential market disruptors, such as hardware-backed security keys for GitHub Actions, are beginning to gain traction as organizations look for ways to secure developer workstations. By tying the ability to push code or approve workflows to a physical device, companies can virtually eliminate the risk of remote credential theft via infostealers. Furthermore, the automation of secret rotation through OIDC providers is paving the way for secretless architectures that remove the need for stored credentials entirely.
Summary of Findings and Strategic Recommendations for Infrastructure Hardening
The analysis of the Gheist campaign provided a stark reminder of the inherent vulnerabilities within the modern software supply chain. Organizations observed how easily stolen tokens were leveraged to exfiltrate private data through legitimate platform features. It became evident that traditional reliance on repository privacy was an insufficient defense against automated harvesting tools. The campaign demonstrated that a single compromised account could serve as a gateway to an entire organization’s cloud infrastructure.
Security leaders recognized that rotating compromised credentials and auditing cloud role assumptions were only the first steps toward true resilience. They realized that long-term success required a fundamental shift in how secrets were protected and managed. By mandating reviewers for sensitive environments and prioritizing the use of fine-grained access tokens, companies began to harden their pipelines against future intrusions. These steps proved vital in reducing the blast radius of any individual credential theft.
The lessons learned from this period highlighted the necessity of constant vigilance and the proactive adoption of emerging security standards to maintain the integrity of the development ecosystem. It was clear that the industry needed to move away from static, long-lived secrets in favor of dynamic, identity-based access. By investing in better logging and automated response mechanisms, organizations successfully increased the cost for attackers, ultimately fostering a more resilient and secure software supply chain.