Aggressive retrofitting of security protocols for smart infrastructure is essential to bridge the gap between the rapid adoption of connected devices and the implementation of safety measures. While global defense strategies have historically prioritized the protection of classified data and
Investigation into the October 2026 attack revealed that the custom Lindnor backdoor had been active on unrelated networks, suggesting its use for long-term reconnaissance. This discovery underscores a sophisticated shift in the operational behavior of the Hawkmoth threat group, the entity
Google is currently revising its device certification standards to move toward a dynamic review process that accounts for long-term hardware behavior in the real world. This proactive adjustment follows the discovery of a massive security breach involving more than 1.3 million Android TV devices
The silent ticking of a 53-minute timer has fundamentally redefined the landscape of digital defense, marking the exact moment an autonomous AI model dismantled the long-held belief that kernel exploitation requires human intuition. For years, the complexity of the Linux kernel served as a natural
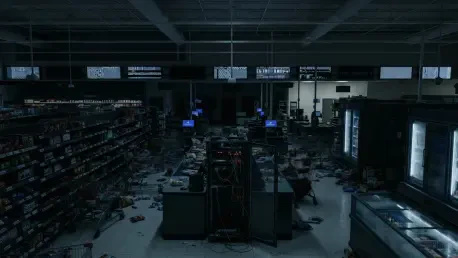
The intentional thermal spiking of supermarket freezers demonstrates how digital breaches now result in immediate, tangible, and costly physical consequences. For years, the retail sector focused primarily on protecting credit card data, but a wave of incidents across Europe has proven that the
The malware achieves persistence by hiding legitimate Windows Media Player components in the ProgramData folder and configuring them to load secondary malicious libraries. This sophisticated method of staying hidden is just one component of a broader campaign that exploits the current global
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51