Digital forensics experts emphasize that simply closing the PHP vulnerability is insufficient if attackers have already planted hidden access points prior to the system update. As the global digital infrastructure approaches the scheduled rollout of emergency patches on October 21, 2026, the stakes
By inspecting the response side of an HTTP transaction, the managed response firewall can detect and intercept anomalous data leaks before they reach a potential attacker's browser. This specific capability marks a significant shift in how edge security providers address deep-seated flaws within
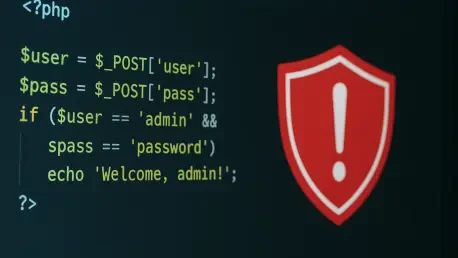
The PHP security advisory highlights that fatal error backtraces on PHP 8.5 should be disabled to prevent specific attack vectors related to stale global state persistence. This warning comes at a critical time for web infrastructure, as the PHP development team recently identified two severe
The speed of this campaign highlights a critical need for defenders to adopt AI-driven monitoring systems to counter the increasing velocity of automated network intrusions. The digital threat landscape underwent a radical transformation as sophisticated threat actors integrated large-scale
Unlike typical software bugs, this kernel-level vulnerability requires only a single malformed packet to compromise the availability of critical enterprise infrastructure. The security community was recently alerted to a zero-day vulnerability, officially cataloged as CVE-2026-70111, which
The sudden realization that a central backup repository has been quietly compromised often serves as the ultimate nightmare for modern IT administrators tasked with safeguarding sensitive corporate intelligence. Recent security disclosures have highlighted a pair of critical zero-day