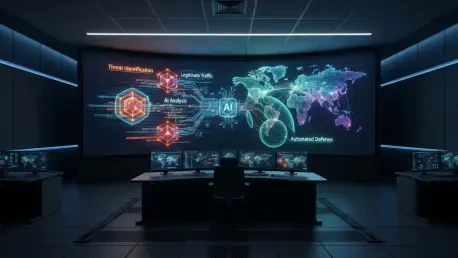
The shift toward AI-driven orchestration serves as a vital tool for reducing analyst burnout by automating the triage of thousands of standard security alerts. This directive, established under Binding Operational Directive 26-04, forces a fundamental rethinking of how the United States federal government approaches its digital boundaries. By moving away from purely reactive methods, the Cybersecurity and Infrastructure Security Agency is pushing Federal Civilian Executive Branch agencies toward a dynamic, risk-based posture that leverages high-speed automation to counter increasingly capable threat actors. This evolution is no longer optional but a survival requirement as the complexity of the global threat environment surpasses human capacity for manual oversight alone. The directive applies not only to federal agencies but also to their cloud service providers operating under FedRAMP authorizations, creating a unified standard for defense across the entire government ecosystem. This transformation underscores the urgent need to align federal defense with the rapid pace of digital shifts.
Adopting Risk-Based Vulnerability Categorization
Historically, federal agencies relied on the Common Vulnerability Scoring System, which prioritized security patches based on static scores that often failed to account for the specific context of an organization’s environment. The transition to the Stakeholder-Specific Vulnerability Categorization (SSVC) model marks a departure from this “one-size-fits-all” methodology, introducing a four-question decision tree that evaluates the actual threat a vulnerability poses. This framework requires security teams to determine if an asset is internet-facing and whether an exploit is being actively automated by adversaries in the wild. By focusing on the technical feasibility of exploitation rather than a generic severity number, agencies can better identify which flaws represent a clear and present danger to their specific mission objectives. This shift ensures that administrative energy is not wasted on low-impact vulnerabilities that lack an exploitation path, allowing for a more surgical and effective defensive response across diverse federal networks.
The adoption of this risk-based approach allows for a strategic concept known as risk-based deferral, which provides agencies the flexibility to manage their remediation backlogs without compromising overall security integrity. By identifying flaws that are unlikely to be exploited—perhaps because they are shielded by internal network controls or lack a public-facing interface—IT departments can prioritize the most critical threats that could lead to immediate system compromise. This prioritization is essential for managing the high volume of security notifications that typically overwhelm federal Security Operations Centers. The SSVC model effectively creates a roadmap for resource allocation, ensuring that human intervention is reserved for high-stakes decision-making while automated systems handle the standard categorization of incoming data. Ultimately, this new focus on environmental context helps bridge the gap between technical vulnerability management and organizational risk management, providing a clearer picture of an agency’s true security posture at any given moment.
Countering the AI-Accelerated Threat Landscape
A primary driver for these updated mandates is the sheer acceleration of the threat landscape, fueled by adversaries who now use artificial intelligence to automate the discovery and weaponization of software flaws. The window between the public disclosure of a vulnerability and its active use in a cyberattack has collapsed from weeks to nearly instantaneous, leaving traditional manual patching cycles hopelessly behind. Threat actors can now scan massive federal networks in a matter of hours, identifying unpatched systems and deploying exploits at a scale previously unimaginable. This rapid evolution means that defensive strategies must transition from human-led responses to machine-speed defense mechanisms to maintain any level of operational security. Without AI-driven tools to assist in identification and response, federal agencies remain vulnerable to breaches that occur before standard administrative processes can even be initiated. This collapsing disclosure-to-exploitation window represents a fundamental shift in the tactical reality facing modern cybersecurity professionals.
In contrast to previous years, modern attackers no longer rely solely on targeted manual efforts but instead deploy automated scripts that can test thousands of entry points simultaneously. This technological leveling of the playing field requires a corresponding upgrade in federal defense capabilities to ensure that security teams are not constantly playing catch-up. The move toward AI-driven defense allows for the real-time analysis of network telemetry, enabling agencies to spot the subtle indicators of an automated probe before it can escalate into a full-scale intrusion. By integrating advanced analytics directly into the defense perimeter, agencies can effectively neutralize automated threats before they find a foothold. This proactive stance is the only viable method for protecting critical infrastructure in an environment where adversaries are increasingly sophisticated and persistent. Consequently, the mandate for automation is not just about efficiency but about building a resilient architecture that can survive the constant pressure of a globally connected and highly automated adversary network.
Sustaining Resilience Through Strategic Modernization
To meet the rigorous compliance deadlines of December 2026, federal Security Operations Centers must integrate continuous asset discovery and automated intelligence correlation into their core workflows. The mandate requires agencies to conduct forensic triage within a strict 24-hour window, a task that is only possible through the use of advanced orchestration tools. This dual requirement of remediating critical flaws within three days while hunting for active intruders ensures that vulnerabilities are not just patched, but thoroughly investigated for signs of prior exploitation. By visualizing asset relationships through contextual graphs, security teams gain the ability to understand the potential business impact of a breach before it can spread. These operational shifts allow for a more strategic allocation of resources, focusing human intervention on high-priority threats while automated systems manage the massive influx of standard telemetry and logging data. These capabilities provide a comprehensive foundation for a modern federal security posture.
The implementation of these AI-driven defenses successfully aligns with strict FedRAMP High baseline controls and NIST SP 800-53 standards, ensuring that national security remains uncompromised throughout the transition. It is established that logical and physical isolation of federal data, alongside strict U.S.-based residency requirements, provides the necessary framework for secure cloud operations. To maintain this posture, agencies are encouraged to audit their automated decision-making processes to ensure accuracy. By restricting network egress to validated domains and utilizing expert oversight from domestic threat hunters, organizations effectively prevent unauthorized data exfiltration. The move toward platform consolidation proves to be a decisive factor in reducing analyst burnout and improving response metrics. Ultimately, federal leaders prioritize the integration of real-time threat intelligence into their orchestration layers to stay ahead of automated adversaries. This proactive approach ensures that networks match the sophistication of modern attacks.