The ubiquity of Quick Response codes across modern urban landscapes has transformed the average smartphone into a high-stakes target for sophisticated cybercriminals in 2026. From digital restaurant menus to contactless payment portals at public transit hubs, these matrix barcodes provide a seamless bridge between the physical and digital worlds. However, this convenience comes with a significant security trade-off that many users overlook during their daily routines. Recent data indicate that approximately forty percent of mobile users have encountered at least one suspicious communication or malicious link within the last quarter. This surge in mobile-centric threats is concerning as smartphones have evolved into primary financial terminals, storing everything from banking credentials to biometric data. As hackers refine their methods to exploit habitual mobile interactions, the distinction between a legitimate service and a fraudulent trap has become increasingly blurred for the average consumer.
1. The Technical Mechanics of Quishing
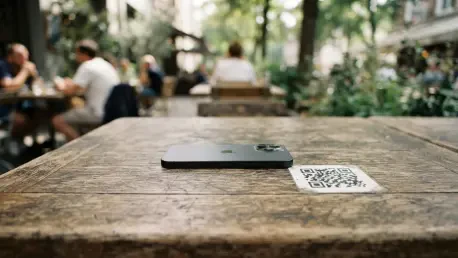
The term quishing refers to QR-code-based phishing, where bad actors replace legitimate codes with malicious versions to redirect users to fraudulent websites. These attacks often involve physical tampering, such as placing a deceptive sticker over a genuine code at a parking meter or cafe. Because QR codes are visually indecipherable, users cannot know if the encoded URL leads to a secure processor or a data-harvesting clone site. This method effectively bypasses email filters designed for text-based links that struggle with embedded images.
Furthermore, the mobile-first nature of these attacks targets devices lacking the robust security software found on corporate workstations. When a user scans a compromised code, the malicious site can attempt to capture credentials or prompt script downloads. The speed of scanning often discourages the caution applied to email links. Consequently, those relying on public infrastructure remain vulnerable to these discreet exploits in high-trust environments. By shifting the attack vector to a personal device, criminals exploit the lack of enterprise-grade firewalls and real-time monitoring tools.
2. Evolution of Mobile Impersonation Tactics
The landscape of mobile fraud has expanded to include the distribution of highly convincing clone applications and investment platforms. Utilizing generative tools, scammers replicate the branding and user interface of financial institutions with near-perfect accuracy. Even official marketplaces face challenges in identifying these clone firms that impersonate authorized businesses to steal data. Once a victim installs a fraudulent app, the software may request extensive permissions that allow criminals to monitor activity or intercept sensitive communications.
In addition, authorized push payment fraud represents a risk where criminals use social engineering to convince targets to initiate transfers themselves. By posing as bank representatives, fraudsters create a sense of urgency that leads victims to bypass security warnings. These schemes often involve capturing one-time passcodes during the transaction to authorize changes to digital wallets. As these tactics become personalized, the psychological pressure often outweighs technical knowledge. Criminals prioritize these methods because they rely on the user to bypass their own bank security protocols voluntarily.
3. Effective Defensive Protocols for Users
Developing a habit of physical and digital inspection is the first line of defense against quishing and mobile scams. Before scanning a code, users should check for signs of tampering like peeling corners or inconsistent textures suggesting an overlay. Most smartphones provide a preview of the destination URL before the browser opens, allowing the user to verify the domain. If a site appears to be a series of random characters or uses an unfamiliar domain, the safest course is to close the application immediately.
For transactions, navigating directly to an official website or using a previously installed banking app is far more secure than following a link. Relying on reputable security software that offers real-time web protection can also block malicious domains before they load. Additionally, using AI-powered detection tools to analyze suspicious links provides an objective second opinion. By diversifying access methods and avoiding untrusted links, mobile users significantly reduce exposure to threats. These technical layers work in tandem with user skepticism to create a much more difficult environment for potential scammers to navigate.
4. Strategic Implementation of Mobile Safeguards
The adoption of comprehensive security measures has proven to be an essential step for individuals looking to protect their digital assets from mobile threats. Users who prioritize the installation of specialized security suites achieve a higher rate of detection for phishing compared to those who rely on native features. These systems identify malicious URLs and block unauthorized data exfiltration in real-time. The application of multi-factor authentication also plays a critical role in preventing access, even when credentials are compromised through fraudulent sites.
Furthermore, the transition toward using verified banking channels rather than third-party redirects significantly decreases the success rate of push payment fraud. Educated consumers who verify the identity of unexpected callers through official support lines avoid the pitfalls of social engineering. The integration of scanning tools allows for the proactive identification of quishing before information is entered into deceptive portals. These behaviors establish a resilient defense that empowers users to navigate the digital landscape with confidence. The move toward hardware-based security keys also provides a future-proof method for securing sensitive financial accounts.