While explicit instructions help an attacker remove legitimate data, the mere presence of forged text is often enough to insert misinformation into a summary. In the current landscape of 2026, professional productivity relies heavily on automated assistants that distill massive communication
Standing access within enterprise networks has become a major vulnerability that red teams and malicious actors have exploited for years. This persistent entry point allows attackers to move laterally with ease, often remaining undetected for extended periods while they map out sensitive digital
The Moroccan state’s response to surveillance allegations involves a coordinated disinformation campaign through pro-government media outlets like Al Barlamane and Le 360. This effort masks a reality where the Direction Générale de la Surveillance du Territoire (DGST) has successfully weaponized
A silent digital infiltration is currently unfolding across the corridors of power in Washington and Tokyo, where elite hackers are systematically dismantling the security barriers once thought to be impenetrable. This operation is not merely a quest for data; it is a calculated strike against the
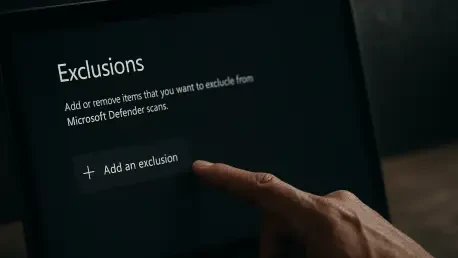
The strategic ROI for a threat actor increases significantly when they can download and unpack ransomware within a zone explicitly ignored by Microsoft Defender. This method of bypassing security protocols represents a sophisticated shift in cyber-adversary tactics, where the tools designed for
Modern cybercriminals are pivoting away from traditional data theft to focus on the financial exhaustion of corporate AI budgets through unauthorized API key exploitation. The emergence of the x47.c botnet, specifically the Fast Flux Edition v4.1 developed by WraithTools, signals a major transition
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61 62 63 64 65 66 67 68 69 70 71 72 73 74 75 76 77 78 79 80 81 82 83 84 85 86