Telecommunications and gaming companies recently faced unprecedented volumetric attacks reaching peaks of 1.38 Tbps and 1.36 Tbps, respectively. These record-breaking events signal a dramatic resurgence in the scale and ferocity of automated cyber threats across the global digital landscape. While
This volatility necessitates a departure from standard security protocols that merely react to incidents after they occur. By moving toward a model of anticipatory engagement, the Cybersecurity and Infrastructure Security Agency aims to neutralize threats before they can compromise vital systems.
By registering fifteen abandoned update domains, security experts were able to push a benign patch that deactivated the flawed mechanism for two million users. This specific security intervention targeted a defunct fork of the popular media streaming application Popcorn Time, which had been left in
The security landscape was recently shaken by the discovery of CVE-2026-111497, a vulnerability known as HTTP2Shell that targets the widely utilized Brotli compression library rather than the application layers themselves. While initial observations suggested the flaw was confined to specific
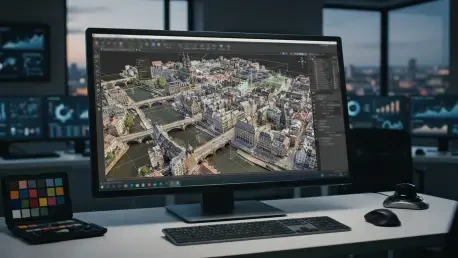
The integration of standalone PLY and OBJ file support simplifies the process of bringing external geometric data into a unified post-processing environment. The release of DJI Modify version 1.7.0 represents a pivotal shift in how drone professionals approach the post-processing of 3D models.
By leveraging the ambient authority of unprotected Docker APIs, the CARBONATO botnet achieves container breakout and executes code directly on the underlying host system. This discovery represents a pivotal moment in 2026, marking the transition from traditional, script-based malicious activity to