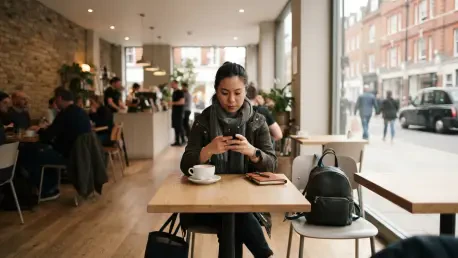
Stepping onto the platform at King’s Cross or finding a quiet corner in a crowded South Kensington cafe, modern travelers almost always pull out their smartphones to check for an available Wi-Fi connection. In the fast-paced environment of 2026, the demand for seamless connectivity has transformed London into a massive digital hub where data flows as constantly as the traffic around Piccadilly Circus. This ubiquity of internet access is a testament to the city’s technological advancement, yet it simultaneously creates a complex web of vulnerabilities for the millions of users who connect to shared hotspots every day. Navigating this landscape requires more than just a device; it necessitates a sophisticated understanding of how data moves through the air and the potential for that data to be intercepted by malicious actors.
London offers a unique digital ecosystem where ancient architecture houses some of the most advanced wireless infrastructure in the world. From the high-speed networks provided within the deep tunnels of the London Underground to the boutique Wi-Fi setups in Shoreditch, the convenience is undeniable for tourists navigating the streets and professionals managing global business from local bars. However, the sheer density of users makes the city a prime target for cybercriminals who exploit the trust people place in familiar-sounding network names. Establishing a secure connection in such a crowded environment is no longer just a luxury for the tech-savvy but a fundamental necessity for anyone wishing to keep their personal information, financial data, and professional correspondence private.
Navigating London’s Digital Landscape Securely
The digital map of London is just as intricate as its physical streets, with thousands of public access points scattered across the capital’s thirty-two boroughs. Whether a person is standing in the shadow of the Shard or enjoying the greenery of Hyde Park, a free connection is usually just a few taps away. This environment has fostered a culture of constant connectivity, enabling digital nomads and students to treat the entire city as their office. While this accessibility drives productivity and enhances the tourist experience, it also introduces a level of exposure that many users underestimate. The variety of network providers, ranging from major telecommunications giants to small independent business owners, means that security standards vary wildly across different locations.
In this sprawling landscape, the threat of an “evil twin” hotspot is particularly prevalent near major transit hubs and popular tourist landmarks. Attackers often deploy these rogue networks in high-traffic areas where people are likely to be distracted and eager for a quick connection. By mimicking the name of a legitimate service, these deceptive access points can trick a device into routing all its internet traffic through a hacker’s laptop. Once a user is connected, the intruder can monitor unencrypted activity, capture login credentials, and even inject malware into the browsing session. Understanding the nuances of this digital terrain is the first step toward building a defense that protects one’s identity from the invisible risks lurking behind the convenience of a free signal.
Maintaining a secure posture in London also involves recognizing the different types of public Wi-Fi available throughout the city. Some networks are fully open, requiring no authentication, while others use a “captive portal” that asks for an email address or a social media login. Each of these entry methods presents its own set of challenges, as even legitimate portals can be spoofed or used to harvest more data than is necessary for a simple internet connection. By staying informed about the current state of wireless security and remaining vigilant in public spaces, individuals can continue to enjoy the benefits of London’s connected infrastructure without falling victim to the various scams that target unsuspecting commuters and visitors.
The Importance of Proactive Wi-Fi Security
Taking a proactive approach to digital security is far more effective than trying to mitigate the damage after a breach has occurred. Currently, the sophistication of data interception tools has reached a point where even a casual observer on a public network can potentially access sensitive information if proper defenses are not in place. Public networks, by their very nature, lack the robust, end-to-end encryption found in home or corporate environments, leaving a window of opportunity for unauthorized access. This vulnerability makes it possible for individuals sharing the same hotspot to see what others are doing, leading to potential identity theft or the compromise of high-value accounts.
Implementing security best practices provides a layered defense that protects multiple facets of a user’s digital life and ensures privacy. For remote workers, this means ensuring that trade secrets and client data remain confidential even when working from a coworking space in Canary Wharf. For students and travelers, it means preventing unauthorized access to social media accounts, email, and banking portals that could be used to facilitate fraud. The financial and emotional cost of recovering a stolen digital identity far outweighs the minimal effort required to secure a connection before browsing. Furthermore, a proactive stance helps to maintain the overall integrity of the city’s digital networks, as fewer compromised devices mean less opportunity for malware to spread through shared connections.
Ultimately, digital security is about empowerment and maintaining control over personal information in an increasingly connected world. When a person takes the time to verify a network or enable a security feature, they are asserting their right to privacy and protecting their future digital footprint. This sense of “digital street smarts” is just as important as physical safety when navigating a global city like London. By adopting a few simple habits, users can ensure that their online interactions remain private, their transactions stay secure, and their overall experience of the city’s technological offerings is both seamless and safe from the ever-evolving threats of the modern era.
Actionable Steps for Staying Safe on Public Networks
Securing a device on a public network does not require an advanced degree in computer science, but it does require a commitment to consistency. The following sections outline practical measures that any user can implement to significantly reduce their risk profile while navigating London’s hotspots. These steps are designed to be integrated into a daily routine, providing a reliable framework for digital safety that remains effective regardless of the location or the type of device being used. By understanding the rationale behind each step, users can better appreciate the value of these habits and ensure they are applied correctly in every situation.
1. You should always verify the identity of the network before connecting to ensure that your device and data remain completely secure at all times
One of the most effective ways to avoid falling for a malicious hotspot is to confirm the exact name of the official Wi-Fi network before attempting to join. In a city where dozens of signals can overlap in a single square mile, the presence of multiple networks with similar names is a common occurrence. Legitimate businesses typically display their Wi-Fi information on signage or provide it upon request from a staff member. Relying on the list of available networks shown by a smartphone can be misleading, as hackers often choose names that appear helpful or official, such as “Free_City_WiFi” or “Guest_Access_Connect,” to lure users into their traps.
Consider a traveler sitting in a crowded cafe near the British Museum who sees two networks, “Cafe_Guest_Free” and “Cafe_Guest_WiFi,” and assumes both are legitimate without verification. By simply asking the barista, the user could discover that the latter is actually a fraudulent network set up by a nearby attacker specifically to capture login credentials from unsuspecting patrons. This simple act of verbal confirmation acts as a powerful barrier against the “evil twin” attacks that are so prevalent in London’s major tourist districts. It is always better to spend a few seconds asking a question than to spend hours dealing with a compromised account.
Furthermore, if a network seems suspicious or behaves in an unusual way, it is often safer to rely on a mobile data connection. Modern cellular networks provide a high level of built-in encryption that is significantly harder to compromise than a standard public Wi-Fi signal. In areas like downtown where network density is high, switching to a 5G connection can provide both better speed and superior security. Developing a habit of skepticism toward any network that does not have a clearly verified identity is a hallmark of a secure digital lifestyle in a busy urban environment.
2. You should prioritize visiting websites that use HTTPS encryption to ensure that your personal information and data remain safe from potential cyber threats
The protocol used to access a website plays a critical role in the security of the data being transmitted, making it essential to ensure that every website visited on public Wi-Fi begins with “https://” instead of the older, unencrypted “https://”. The “S” at the end stands for “secure” and indicates that the communication between the browser and the web server is encrypted. This encryption layer ensures that even if someone on the same network manages to intercept the data packets, they will be unable to read sensitive information, such as passwords, credit card numbers, or private messages.
For instance, when a tourist uses a hotel’s shared Wi-Fi in Central London to book a theater ticket, the use of the HTTPS protocol is what keeps their transaction details safe. The encryption prevents the hotel network operator, other guests, or potential hackers from seeing the payment information or the user’s personal details during the booking process. Most modern browsers now include visual indicators, such as a padlock icon in the address bar, to help users quickly identify whether a connection is secure. If a browser displays a warning about a website’s security certificate, it is a clear sign to disconnect and avoid entering any sensitive information.
While the majority of high-profile websites have moved to HTTPS by default, some older or less-maintained sites may still use unencrypted connections. In these cases, users should exercise extreme caution and avoid performing any actions that require a login or the entry of personal data. There are also browser extensions available that automatically redirect users to the secure version of a website whenever possible. By making HTTPS a non-negotiable requirement for browsing, individuals can create a much safer online experience that minimizes the risk of data sniffing and other forms of network-based eavesdropping.
3. Maintain Up-to-Date Software and Applications
The security of a device is only as strong as its most vulnerable piece of software, and cybercriminals are constantly looking for weaknesses in operating systems and applications that they can exploit to gain unauthorized access to a user’s data. Software developers respond to these threats by releasing security patches and updates that close these vulnerabilities and strengthen the device’s overall defenses. Neglecting these updates leaves a device open to known exploits that can be easily executed by anyone with basic hacking tools on a shared network.
A remote professional working from different locations across London can benefit significantly from enabling “Automatic Updates” on their laptop and mobile devices. This ensures that the system always has the latest protection against emerging threats, even if the user is busy traveling between meetings and forgets to check for updates manually. When a device is fully patched, it is much harder for malware to gain a foothold, even if the user accidentally connects to a subpar network in a coworking space or a train station. This proactive maintenance is a simple but highly effective way to stay ahead of those who look for easy targets on public Wi-Fi.
In addition to the operating system, it is vital to keep individual applications updated, especially browsers and communication tools. These programs serve as the primary interface through which users interact with the internet, making them frequent targets for cyberattacks. Regularly checking for updates before a business trip or a long day of sightseeing ensures that a device is in the best possible condition to withstand any security challenges it might encounter. Investing a few minutes in software maintenance provides a high return in terms of long-term digital safety and peace of mind.
4. You should disable the automatic Wi-Fi connection features on your devices to ensure that you do not inadvertently connect to potentially malicious or unsecured wireless networks
Convenience often comes at the cost of security, and the automatic Wi-Fi connection feature found on most modern devices is a prime example. While it is helpful for a phone to automatically join a home or office network, this feature can be a major liability in a public setting. Devices configured to “auto-join” remembered networks can be easily tricked by a malicious hotspot broadcasting a familiar Service Set Identifier (SSID). An attacker can set up a rogue access point with a common name like “NYC_Free_WiFi,” and any nearby device that has previously connected to a network with that name might attempt to join it without the user’s knowledge.
This risk is particularly high at major hubs like Heathrow Airport, where thousands of people pass through daily, many of whom may have used a network with a generic name in another city or country. By disabling the auto-join feature, a user prevents their phone or laptop from making unintended connections to potentially malicious spoofed networks in the terminal. Instead, the device will ask for permission before joining any new network, giving the user a chance to verify the connection’s legitimacy. This small change in settings significantly reduces the attack surface of the device and puts the user back in control of their connectivity.
Reviewing the list of saved networks periodically is a good practice for maintaining digital hygiene, as removing old or generic networks that are no longer needed ensures that a device does not attempt to reconnect to them in the future. In a city like London, where one might connect to dozens of different hotspots over the course of a week, keeping the saved network list organized is a manageable way to reduce unnecessary exposure. By being deliberate about every connection, a user can navigate the city’s digital landscape with much greater confidence and security.
5. Implement Two-Factor Authentication (2FA)
Even the most robust password can be compromised through phishing or data interception, which is why two-factor authentication has become a critical component of modern digital security. By requiring a second form of identification, such as a code from an authenticator app, a physical security key, or a push notification on a trusted device, 2FA ensures that a password alone is not enough to gain access to an account. This extra layer of protection is especially important for high-value accounts that contain sensitive personal, financial, or academic information.
A student accessing their university portal via public Wi-Fi at the British Library can rest easier knowing that their account is protected by 2FA. Even in the unlikely event that a sophisticated hacker manages to capture their password through a rogue hotspot, the account remains inaccessible because the attacker cannot provide the unique, time-sensitive code generated on the student’s smartphone. This secondary barrier effectively nullifies the value of a stolen password and provides the user with an immediate warning if someone else attempts to log in to their account.
Most major online services, including email providers, social media platforms, and banking institutions, now offer various forms of 2FA. While some people might find the extra step slightly inconvenient, the security benefits far outweigh the minor delay in the login process. For those who frequently use public Wi-Fi, 2FA is one of the most powerful tools available for preventing account takeovers and protecting a digital identity. Setting it up on all critical accounts is a one-time task that provides continuous protection against a wide range of cyber threats.
6. Restrict file sharing and network discovery settings to prevent unauthorized users from accessing your sensitive data over the local network
When a device connects to a public Wi-Fi network, it effectively becomes part of a local community of devices that can sometimes “see” and interact with one another. Many operating systems have features enabled by default that allow for easy file sharing and network discovery, which are useful in a trusted home environment but dangerous in a public cafe. If these settings are left on, a stranger on the same network could potentially see shared folders, access print services, or even attempt to view the device’s screen. Restricting these features is an essential step in making a device “invisible” to others on a public hotspot.
Before opening a confidential work presentation in a SoHo coffee shop, a freelancer should take a moment to adjust their device’s sharing settings. On a MacBook, this involves going into System Settings and toggling off options like File Sharing, Screen Sharing, and printer access. Windows users can achieve a similar result by selecting the Public network profile when prompted, which automatically applies more restrictive firewall rules and disables network discovery. These actions ensure that the device remains isolated from other users on the network, preventing unauthorized access to local files and services.
This layer of defense is particularly important for those who handle sensitive client data or proprietary business information. In a busy urban environment where many people work side by side, it is easy to forget that a shared internet connection is not a private one. By taking the time to secure these internal settings, a user can create a “digital bubble” around their device, allowing them to work effectively without worrying about who might be trying to peek into their local system. It is a simple technical adjustment that provides a significant boost to a person’s overall security posture.
7. Utilizing a Virtual Private Network (VPN) remains one of the most effective methods for securing your internet connection and protecting your sensitive personal data from potential cyber threats
A Virtual Private Network is often considered the final and most comprehensive layer of defense for anyone using public Wi-Fi. A VPN works by creating an encrypted tunnel for all of a device’s internet traffic, effectively masking the user’s activity from the local network provider and anyone else who might be monitoring the connection. This means that even if the Wi-Fi network itself is unencrypted or managed by a malicious actor, the data inside the VPN tunnel remains secure and private. It also hides the user’s IP address, providing an additional layer of anonymity while browsing.
For a digital nomad navigating the various neighborhoods of London, using a tool like X-VPN ensures that their data remains private as they move between different hotspots throughout the day. By downloading and activating the VPN before their trip, the traveler can ensure that every connection they make—whether in a hotel, an airport, or a local cafe—is wrapped in a layer of enterprise-grade encryption. This is especially useful for those who need to access corporate networks or handle sensitive transactions while on the move. The VPN provides a consistent level of security that does not depend on the quality of the underlying Wi-Fi connection.
In 2026, many VPN services have become incredibly user-friendly, offering one-click connections and high-speed servers that do not noticeably slow down the internet experience. While there are many options available, it is important to choose a reputable provider that has a clear privacy policy and a strong track record of protecting user data. Using a VPN should be seen as a standard part of a person’s digital toolkit, providing a reliable and portable security solution that works anywhere in the world. It is the ultimate safeguard for those who refuse to compromise on their privacy while enjoying the convenience of a connected city.
Final Evaluation: Balancing Convenience and Security
The exploration of London’s digital landscape demonstrated that staying safe on public Wi-Fi required a blend of technical tools and informed decision-making. Users who adopted a proactive stance found that the risks associated with shared hotspots were manageable when approached with a sense of digital street smarts. The guide emphasized that no single solution was foolproof; instead, it was the combination of verifying networks, using encrypted protocols, and maintaining updated software that created a resilient defense. These habits allowed people to navigate the city’s vast network of hotspots without sacrificing their personal privacy or the security of their sensitive accounts.
The analysis of current trends indicated that the future of urban connectivity would rely even more heavily on pervasive wireless access, making these security foundations more relevant than ever. Implementing these strategies ensured that travelers and remote workers could enjoy a seamless digital experience while moving between various neighborhoods. Those who utilized tools like X-VPN observed a significant increase in their connection privacy, shielding their data from potential interception on less secure public networks. By establishing these practices as standard behavior, individuals were able to protect their digital identities against the most common threats found in high-traffic urban areas.
As technology continued to evolve, the importance of maintaining a layered security approach became a central theme for anyone working or traveling in London. The successful adoption of multi-factor authentication and the restriction of network sharing services proved to be effective barriers against unauthorized access. This comprehensive guide provided the necessary insights for balancing the immense convenience of a connected city with the vital need for data protection. Ultimately, the transition toward a more secure digital lifestyle empowered users to take full advantage of London’s infrastructure while ensuring that their personal information remained exactly where it belonged—in their own hands.