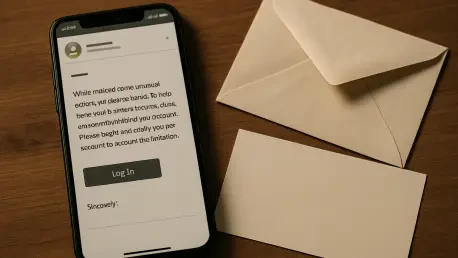
In the current digital landscape, the sophistication of social engineering has reached a point where even tech-savvy users find themselves momentarily paralyzed by a well-crafted notification. The Federal Trade Commission warns that legitimate companies do not send links via email or text message to update private payment information. This simple directive serves as the primary defense against an ever-evolving tide of digital deception that specifically targets users of major financial platforms. When a message arrives claiming that an account is restricted or an unauthorized transaction has occurred, the initial impulse is often to click a button to resolve the issue immediately. However, this reactionary behavior is exactly what cybercriminals count on, utilizing the PayPal brand to lend a veneer of institutional authority to their fraudulent schemes. By understanding the core mechanics of these attacks, individuals can transform from potential victims into informed defenders of their own digital sovereignty, ensuring that personal financial data remains within secured environments rather than falling into the hands of remote opportunistic actors who specialize in exploiting urgency and fear.
1. Refrain From Clicking, Calling, or Responding
Maintaining a strict policy of non-engagement is the single most effective way to neutralize a phishing attempt before it can escalate into a security breach. When a suspicious text or email appears, it often contains high-pressure language designed to bypass critical thinking, such as warnings about account suspension or fraudulent charges that require immediate “verification.” It is imperative to avoid using any buttons or links embedded within these messages, as they are frequently directed to cloned websites that mirror the official login portal with unsettling accuracy. These sites are designed solely to harvest credentials in real time, allowing attackers to hijack accounts before the user even realizes they have been misled. Furthermore, clicking such links can sometimes trigger the download of background scripts or tracking cookies that compromise the privacy of the browser environment. The safest path is to treat every unsolicited message with a high degree of skepticism, recognizing that the medium itself is a red flag regardless of how convincing the branding or the sender’s display name might appear to be.
The danger of interaction extends beyond just clicking links; it includes any form of response, even those that seem designed to opt-out of future communications. Replying to a suspicious text message with the word “STOP” might seem like a logical way to reduce spam, but in the context of a phishing campaign, this action serves as a “proof of life” for the sender. It confirms that the phone number is active and that a human being is reading the messages, which often leads to an increase in targeted attacks or the sale of that specific contact information to other fraudulent networks. Similarly, calling a phone number provided within the body of a suspicious message is a significant risk. These numbers do not lead to legitimate customer support centers but rather to social engineering specialists who use voice-over-IP technology to appear local or official. These individuals are trained to extract one-time passwords, social security numbers, or even convince users to install remote access software under the guise of technical support. Temporarily saving the message for the purpose of reporting it to authorities is the only reason to keep it on a device.
2. Access Your Account Independently
Verification of any account-related claim must always occur through channels that are completely isolated from the suspicious message itself. This means navigating to the official PayPal website by manually typing the URL into the browser’s address bar or utilizing the official mobile application that was previously installed from a verified app store. By taking this proactive step, a user ensures that the connection is encrypted and directed to the genuine servers of the service provider, bypassing any redirects or DNS poisoning that might be associated with a phishing link. It is a common mistake to rely on search engine results for a company’s login page, as malicious actors sometimes purchase advertisements that appear at the top of search results, leading to further fraudulent sites. Directly entering the web address is a fundamental habit that eliminates the possibility of being diverted to a deceptive landing page. Once the secure connection is established, the user can log in with confidence, knowing that any legitimate issues will be clearly documented within the internal notification system of the platform.
Once inside the official account dashboard, the discrepancy between the phishing message and reality usually becomes immediately apparent. Users should carefully review their recent transaction history, pending invoices, and the notification bell icon to see if any of the claims made in the message are reflected in the actual account data. If the message claimed there was a “suspicious transaction” or an “unpaid invoice,” but the internal history shows no such activity, the message can be definitively classified as a scam. Legitimate financial institutions provide detailed internal logs for every action taken on an account, and these records are the only source of truth. If a genuine problem exists, the platform will typically provide a secure way to resolve it within the dashboard, such as a resolution center or a dedicated support ticket system. This method of independent verification effectively breaks the cycle of fear that scammers rely on, as it replaces the uncertainty of a text message with the concrete, verifiable data provided by the service’s official infrastructure.
3. Submit a Report of the Incident
Turning a fraudulent interaction into a tool for broader prevention involves utilizing established reporting channels that help authorities map the scope of current campaigns. For those who encounter a suspicious email, forwarding the entire message to reportphishing@apwg.org provides the Anti-Phishing Working Group with critical metadata needed to identify and neutralize malicious servers. Similarly, text-based threats should be forwarded to the shortcode 7726, a universal reporting number used by mobile carriers to flag and block spam numbers across their networks. These actions do more than just clean up a personal inbox; they contribute to a massive database of threat intelligence that security researchers use to develop more robust filters for everyone. By taking sixty seconds to forward a message before deleting it, a user effectively participates in a community-wide effort to dismantle the infrastructure that supports these scams, making it more expensive and difficult for bad actors to reach their next target in the future.
Beyond reporting to technical groups and carriers, it is vital to notify the Federal Trade Commission through their dedicated portal at ReportFraud.ftc.gov. This agency tracks the economic impact of fraud and uses the data to issue public warnings and coordinate with law enforcement to take down large-scale operations. While the FTC may not investigate every individual report, the cumulative data allows them to identify patterns and target the most damaging fraud networks currently operating. Once the report is filed, the user should proceed to block the sender’s email address or phone number through their device’s native settings. This prevents the same attacker from attempting a follow-up or a “recovery” scam, where they pretend to be a security firm offering to fix the very problem they created. Erasing the message after reporting it ensures that no one else in the household accidentally clicks a live link and removes the psychological clutter of the attempted deception from the user’s daily digital experience.
4. Update Your Credentials if You Shared Information
If a lapse in judgment led to the disclosure of a password or other sensitive login data on a suspicious page, the window for mitigation is often measured in minutes. The primary step is to change the compromised password immediately through the official PayPal website, ensuring the new credential is long, complex, and unique. It is not enough to change the password on the targeted platform alone; because many users recycle passwords across different services, any other account sharing those same credentials must also be updated. This includes email accounts, social media profiles, and especially banking websites. Attackers frequently use automated tools to “credential stuff,” attempting the stolen username and password combination on hundreds of other popular sites within seconds of the initial theft. Securing the primary email account associated with the financial platform is particularly critical, as it often serves as the gateway for password resets and identity verification across the entire digital life of the user.
In addition to changing passwords, enabling multi-factor authentication (MFA) provides a necessary layer of defense that remains effective even if a password is stolen in the future. MFA requires a second form of verification, such as a code from an authenticator app or a physical security key, making it exponentially harder for an unauthorized party to gain access to the account. While updating these settings, the user should also perform a comprehensive audit of their account profile to ensure no unauthorized changes were made. Scammers often attempt to add their own email addresses or phone numbers to the account recovery options to maintain access after a password change. Checking for new “authorized devices” or “linked apps” within the security settings can reveal if an attacker has already established a foothold. Removing these unrecognized entries and confirming that all contact information is accurate ensures that the user retains full control over the account’s security infrastructure and future recovery attempts.
5. Eliminate Suspicious Software or Profiles
Mobile devices require a specific set of checks to ensure that a phishing interaction did not result in the installation of persistent malicious software. On an iPhone, the threat often comes in the form of a configuration profile rather than a traditional application. These profiles can be used to redirect web traffic through a malicious proxy or to install unauthorized certificates that compromise encrypted communications. Users should navigate to the “General” section of their iOS settings and look for a menu labeled “VPN & Device Management.” If any profiles appear there that were not intentionally installed by the user or their employer, they should be removed immediately. Furthermore, any unfamiliar apps that appear on the home screen after a suspicious interaction should be deleted by long-pressing the icon and selecting the removal option. Apple’s sandboxing architecture provides significant protection, but the manual installation of a profile can bypass many of these safeguards, making this manual check a critical step in a post-phishing security audit.
Android users must navigate a different set of protocols to ensure that no malicious payloads remain active on their hardware after an encounter with a phishing site. If an application was installed during the interaction, the standard uninstallation process via the system settings is the first line of defense. However, in cases where the “Uninstall” button appears grayed out or inactive, it is likely that the malicious software has gained administrative privileges to prevent its own removal. To rectify this, the user must navigate to the security section of their settings and locate the menu for “Device admin apps,” where they can manually revoke any permissions granted to unfamiliar entries. Once these administrative rights are stripped away, the application can be removed through the traditional interface without further resistance. This granular control over application permissions is essential for maintaining the integrity of the Android ecosystem, particularly when dealing with sophisticated malware that attempts to hide in plain sight by mimicking system utilities or legitimate security tools.
6. Deactivate Installations From Unverified Sources
The most effective way to prevent the accidental installation of malware on an Android device is to strictly control the sources from which software can be added. Modern versions of the operating system allow users to toggle the “Install unknown apps” permission for individual applications, such as web browsers and messaging platforms. By ensuring this feature is disabled for all apps except for verified sources like the Google Play Store, the user creates a significant barrier against “drive-by” downloads. This protection ensures that even if a user accidentally taps a “Download” button on a fraudulent website, the system will block the execution of the file and alert the user to the potential risk. This setting acts as a critical safety net, providing a final moment of intervention that can prevent a lapse in online judgment from turning into a full device compromise. Regularly auditing these permissions in the system settings ensures that the device remains in a hardened state against the latest delivery methods used by cybercriminals.
Messaging apps have become a primary vector for the distribution of malicious files, often disguised as PDFs or image attachments that supposedly contain “invoice details” or “security reports.” By maintaining the restriction on unknown app installations, the user ensures that even if they open a malicious attachment, the payload cannot pivot to installing a permanent backdoor or a credential-stealing utility. This defensive posture is especially important in an era where phishing attacks are increasingly personalized and difficult to distinguish from legitimate business communications. Beyond just deactivating the installation permission, users should also clear their browser’s cache and data after visiting a suspicious site to remove any temporary scripts or malicious cookies that might have been stored. This “digital hygiene” approach reduces the attack surface of the device and ensures that the web environment remains clean and predictable. Combining restrictive installation settings with regular cache clearing provides a robust defense-in-depth strategy for any mobile user navigating the modern web.
7. Contact Financial Institutions Regarding Lost Funds
When a phishing attack successfully results in the unauthorized movement of money, the speed of the response directly correlates with the likelihood of recovering the funds. The first point of contact should be the financial institution associated with the compromised payment method, whether it is a bank or a credit card provider. Using the official phone number found on the back of the physical card or the bank’s verified website ensures that the user is speaking with the legitimate fraud department. It is crucial to explain that the loss was the result of a phishing scam, as this information allows the bank to initiate the appropriate “chargeback” or “stop payment” procedures. Financial institutions often have specialized protocols for different types of electronic fraud, and providing them with a clear timeline of events can help them freeze the stolen money before it is moved into harder-to-track assets like cryptocurrency or international wire transfers.
Following the initial contact with the bank, filing a formal complaint with the FBI through the Internet Crime Complaint Center at ic3.gov provides a legal record of the theft. While the FBI does not personally investigate every local case, they aggregate this data to track the movement of stolen funds across state and international lines, sometimes leading to the seizure of criminal assets. For victims who have lost more than just money—such as those who provided a Social Security number or other identifiers—the website IdentityTheft.gov offers a customized recovery plan. This service helps users place fraud alerts on their credit reports and provides the necessary documentation to prove that their identity has been compromised. These steps are vital for protecting a user’s long-term financial reputation and preventing secondary fraud, such as the opening of unauthorized credit lines. Dealing with the aftermath of a successful phishing attack is a multi-step process, but following these established legal and financial protocols provides the best possible path toward restitution and future protection.
8. Verify Your PayPal Account Securely
Developing a standardized method for checking account health is the most reliable way to avoid the pitfalls of social engineering. Users should commit to using only trusted entry points, which include manually saved bookmarks or the official application provided by the service. This practice eliminates the need to ever trust an incoming link, regardless of how official it looks. By establishing a routine where the user only interacts with their financial data through these pre-verified channels, the power of a phishing message is completely neutralized. The attacker’s primary weapon is the “link,” and by refusing to use it, the user remains in complete control of the digital environment. This habit also encourages a more deliberate approach to online finance, where transactions are reviewed on the user’s terms rather than in response to a simulated emergency created by a malicious third party.
In addition to using trusted entry points, users should become familiar with how legitimate notifications are delivered within the secure account environment. Most major platforms, including PayPal, utilize an internal message center or a notification bell icon to alert users to legitimate account issues, disputes, or security warnings. If a text message claims there is a “case number” or an “active dispute,” but the internal resolution center shows no such activity, the user has definitive proof of fraud. These internal systems are designed to be the primary source of communication, and they are significantly more secure than SMS or email. Checking these notifications regularly allows users to stay informed about their account status without exposing themselves to external risks. Understanding the difference between a high-pressure external message and a professional internal notification is a key component of modern digital literacy, allowing users to navigate their financial lives with a high degree of confidence and security.
9. Moving Toward a More Secure Digital Future
The broader ecosystem of digital payments reached a critical juncture where the responsibility for security shifted from passive observation to active participation. Users who successfully navigated these threats often found that the most effective tool in their possession was not a specific software suite, but a disciplined approach to information verification. By prioritizing the use of official applications and direct browser entries, people effectively bypassed the primary entry point for the vast majority of social engineering attempts. The integration of multi-factor authentication and regular security audits became the baseline for maintaining financial health in an environment where static passwords no longer provided sufficient protection. These proactive measures established a defensive perimeter that proved resilient against both traditional phishing and more modern, automated delivery methods that sought to exploit minor lapses in judgment or attention.
As the sophistication of fraudulent tactics continued to grow, the importance of community reporting and institutional cooperation became more evident than ever before. The process of forwarding malicious texts to 7726 and reporting emails to the APWG provided the necessary data for carriers and security providers to sharpen their filters and protect vulnerable populations. Financial institutions, in turn, refined their recovery protocols and improved the transparency of their internal notification systems to help users distinguish reality from deception. This collective effort transformed the internet into a more hostile environment for scammers, as the “success rate” of automated phishing campaigns began to decline in the face of an increasingly informed public. By adhering to these structured safety protocols, individuals not only protected their own assets but also contributed to a global culture of cybersecurity that prioritized facts over fear and verification over blind trust.