Systemic cybersecurity failures have been linked to worsened survival rates for cardiac arrests due to delayed emergency responses and diagnostic bottlenecks in compromised hospitals. The rapid digitalization of healthcare has revolutionized the surgical landscape, moving the field away from isolated manual procedures toward a highly integrated ecosystem known as the Surgical Internet of Medical Things (SIoMT). This smart operating room is no longer a self-contained unit but a node in a global digital network. The benefits are significant—real-time data telemetry, remote consultation, and automated monitoring—but the reliance on continuous network connectivity means that even minor digital disruptions can derail complex clinical pathways. Surgical care is uniquely time-sensitive; therefore, any delay in accessing patient schedules or diagnostic images can compromise the integrity of the entire perioperative workflow. Connectivity enhances precision but introduces a fragile digital layer that threatens the safety of patients during their most vulnerable moments.
Identifying Major Risks and Clinical Outcomes
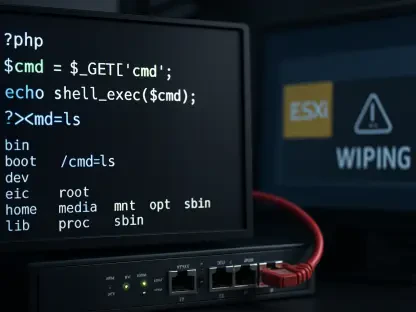
The taxonomy of cyber threats facing the SIoMT ranges from large-scale network shutdowns to targeted hardware interference. Ransomware remains a primary concern for hospital administrators, as it can lock down life-critical systems and force the cancellation of urgent operations on a massive scale. When a facility’s network is encrypted by malicious actors, the resulting paralysis often extends to imaging systems and pathology results, making it impossible to proceed with elective or even semi-urgent procedures safely. Furthermore, the increasing use of wireless devices in the operating room creates opportunities for man-in-the-middle attacks, while vulnerabilities in device firmware or disruptions in the digital supply chain can lead to widespread hardware failure. Even teleoperated robotic platforms face risks, including the potential for malicious actors to manipulate movements or disable systems mid-procedure, bypassing the safety protocols that protect patients during surgery.
The clinical consequences of cybersecurity breaches are profound, often resulting in mass cancellations of procedural admissions and delays in urgent treatments like cancer surgeries. Data suggests a correlation between healthcare network compromises and worsened survival rates for cardiac arrests, likely due to diagnostic bottlenecks and emergency response delays that occur when systems go offline. However, much of this harm may be underreported, as many digital glitches in the operating room are not currently categorized as cybersecurity incidents by the staff involved. This suggests that the true scale of the problem is not yet fully understood, and the current evidence may only represent the tip of the iceberg. Establishing dedicated registries to track these digital near-misses is essential for building a safer healthcare infrastructure. Without a standardized way to document these events, the medical community will continue to struggle with assessing the real-world impact of cyber instability.
Addressing Hardware Vulnerabilities and Strategic Governance
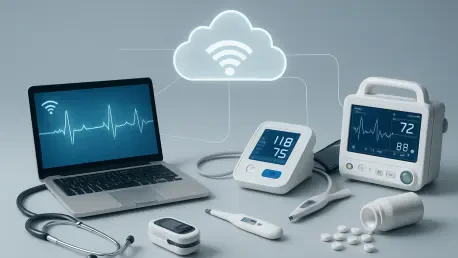
Specific attack surfaces within the operating room present unique challenges for maintaining patient safety in an era of total connectivity. Robotic surgical systems require high-bandwidth connections that are susceptible to command delays or packet injection, while digital infusion pumps can be manipulated to deliver incorrect medication dosages. Furthermore, cardiac implantable electronic devices and perioperative monitors are at risk; if these systems are compromised, clinicians may receive falsified physiological data, leading to dangerous medical errors or unauthorized remote access to life-sustaining equipment. For instance, an anesthesiologist relying on a compromised monitor might fail to respond to a genuine crisis because the displayed data suggests stability. These devices are difficult to secure because their firmware is proprietary and rarely updated with the same frequency as standard computer software. Protecting these critical assets requires a collaborative effort between manufacturers and hospital IT staff.
Institutional leaders foster a culture of cyber-literacy among surgeons and anesthesiologists, ensuring that technical security protocols do not impede the necessary speed of clinical care. They transition away from fragmented regulatory policies toward a unified secure-by-design engineering approach that integrates cybersecurity into the initial manufacturing of medical devices. This strategy includes the development of specialty-specific threat models tailored to the unique demands of the surgical environment. Standardized registries are established to document and learn from digital near-misses, providing the transparency required to improve system resilience. Medical device manufacturers prioritize long-term firmware support and maintain transparency regarding the security of their connected platforms. This collective responsibility ensures that the risks associated with the surgical internet are managed with the same rigor as traditional surgical complications, which ultimately protects the safety of all patients involved.