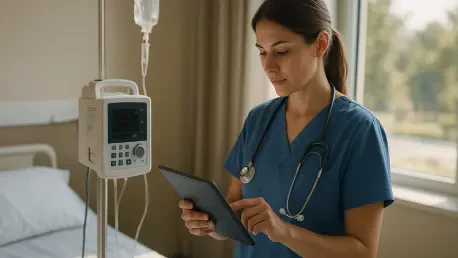
Adding complex encryption to federated learning rounds can introduce delays of nearly eighteen seconds, which is unsuitable for life-critical medical interventions. In the rapidly evolving technological landscape of 2026, the Internet of Medical Things has become the backbone of modern clinical environments, yet this reliance exposes a dangerous friction between patient safety and data protection. Federated Learning provides a promising middle ground by allowing artificial intelligence models to train across decentralized hospital networks without ever moving raw patient records. This method effectively mitigates the risk of massive data breaches that once plagued centralized repositories, but it also creates a new, decentralized theater for cyber warfare. Recent systematic reviews of over one hundred peer-reviewed studies published through late 2025 demonstrate that while the data itself stays private, the very mechanism of sharing model updates introduces unique vulnerabilities. The challenge lies in securing these communications without compromising the real-time responsiveness required by medical devices.
Understanding the Vulnerabilities of Decentralized Healthcare
The Architectural Risks: IoMT and Federated Learning
The physical architecture of the Internet of Medical Things consists of a vast and diverse ecosystem ranging from implanted cardiac monitors to high-resolution imaging suites. Each of these devices serves as a node within a federated network, contributing local intelligence to a global diagnostic model. However, this distributed structure fundamentally expands the attack surface for malicious actors who no longer need to penetrate a single high-security vault. Instead, they can target the communication links between the edge devices and the aggregation server, or even compromise a single peripheral sensor to inject faulty data. The primary risk in this setup is the implicit trust that the central aggregator must place in the contributions of its many participants. If even one hospital node is compromised by an adversary, the entire global model can be skewed by subtle, incremental updates that are difficult to distinguish from legitimate clinical variations in patient health metrics.
Communication protocols in these environments are often optimized for speed rather than deep security, leading to significant vulnerabilities during the parameter exchange phase. When a local device finishes training its segment of the model, it transmits gradients to a central server. Attackers can intercept these transmissions to perform reconstruction attacks, effectively reverse-engineering sensitive patient data from the mathematical updates themselves. Furthermore, the lack of centralized oversight means that a rogue node can remain undetected for long periods while slowly degrading the accuracy of the global model. This architectural weakness is particularly concerning in 2026, as medical institutions increasingly rely on automated diagnostic tools to manage high patient volumes. The decentralized nature of the system, while excellent for privacy, removes the traditional “gatekeeper” role, making it difficult to verify the integrity of every participant in the federated training round.
Emergent Threats: Poisoning and Manipulation
The most pervasive threats identified in current medical networks are poisoning attacks, which are broadly categorized into data and model manipulation. Data poisoning involves altering local training samples at the source, such as “label flipping,” where a healthy diagnostic scan is intentionally marked as diseased. This misleads the learning process, causing the global model to produce false positives or negatives when deployed in a clinical setting. Clean-label attacks are even more sophisticated, as the manipulated data appears perfectly legitimate to standard verification tools but contains subtle perturbations that trigger specific model failures. In the high-stakes environment of 2026 healthcare, these attacks can lead to catastrophic medical errors, ranging from incorrect pharmaceutical dosages to unnecessary surgical interventions, all while the system appears to be operating within normal parameters.
Model poisoning represents an even more aggressive vector of attack, as the adversary directly injects crafted gradients or parameters into the aggregation server. This skips the data manipulation step entirely and targets the mathematical foundations of the global intelligence. These interventions can have immediate and devastating effects on model performance, potentially causing a complete collapse of the diagnostic system across an entire hospital network. Beyond simple degradation, stealthy “backdoor” attacks can insert hidden triggers into the model. A backdoor might cause a cardiovascular monitoring system to behave normally under most conditions but fail to trigger an alarm when a specific, rare pattern is presented. Such targeted failures are extremely difficult to detect because the model maintains high overall accuracy, hiding its malicious behavior until the exact moment the trigger is activated.
Implementing Multi-Layered Security Strategies
Robust Aggregation: Defending the Central Node
To counter these sophisticated threats, the industry is moving toward robust aggregation rules that replace traditional mathematical averaging. Algorithms such as Krum, Multi-Krum, and Trimmed Mean are specifically designed to identify and isolate anomalous updates before they are incorporated into the global model. These rules work by calculating the statistical distance between different client updates, effectively filtering out “Byzantine” contributions that deviate too far from the consensus. By identifying these outliers, the central server can maintain the integrity of the learning process even when multiple nodes are providing inconsistent or intentionally deceptive information. In current 2026 deployments, these robust rules serve as the first line of defense against both Sybil attacks and coordinate-level model poisoning, ensuring that no single malicious actor can gain disproportionate influence.
However, the implementation of robust aggregation is complicated by the inherent diversity of medical data. Information gathered from different hospitals or geographic regions is often non-IID, meaning it varies naturally based on local demographics, equipment calibrations, and clinical practices. This heterogeneity makes it difficult for automated security systems to distinguish between a “malicious” update and a “unique but legitimate” clinical case. For instance, a specialized oncology center might produce model updates that look like outliers compared to a general practitioner’s office. To address this, current research focuses on adaptive aggregation techniques that can learn the “normal” range of variation for specific medical contexts. This allows the system to remain sensitive to genuine threats while reducing the rate of false rejections that could strip the global model of valuable, rare medical insights.
Strategic Solutions: Blockchain and Future Resilience
The integration of blockchain technology and advanced privacy-preserving methods has provided a secondary layer of security for the Internet of Medical Things. Blockchain serves as a decentralized, immutable ledger that logs every model update, providing complete traceability and preventing unauthorized participants from joining the federated network. This ensures that every contribution can be audited and linked to a verified medical institution, significantly raising the cost and complexity for an attacker attempting a Sybil or identity-spoofing attack. When combined with homomorphic encryption, these systems allow the central server to aggregate updates while they are still in an encrypted state. This prevents “gradient leakage,” where an adversary might attempt to reconstruct private patient information from the shared model parameters, thereby maintaining the highest standards of confidentiality.
Securing the future of medical artificial intelligence required a departure from purely theoretical security models toward systems that understood the messy reality of healthcare. Developers began prioritizing explainable rejection criteria, which allowed clinicians to understand why certain updates were flagged as malicious rather than relying on opaque, black-box algorithms. This shift toward transparency was coupled with the integration of hybrid defense models that balanced the necessity of privacy with the critical need for threat visibility. By moving away from standardized laboratory datasets and adopting heterogeneous, real-world clinical benchmarks, the industry addressed the critical performance gaps identified in earlier research. Ultimately, the successful implementation of secure federated learning relied on a holistic integration of safeguards across the device, communication, and decision-making layers. These coordinated efforts ensured that the IoMT delivered on its promise of safe, private, and hyper-accurate clinical care.